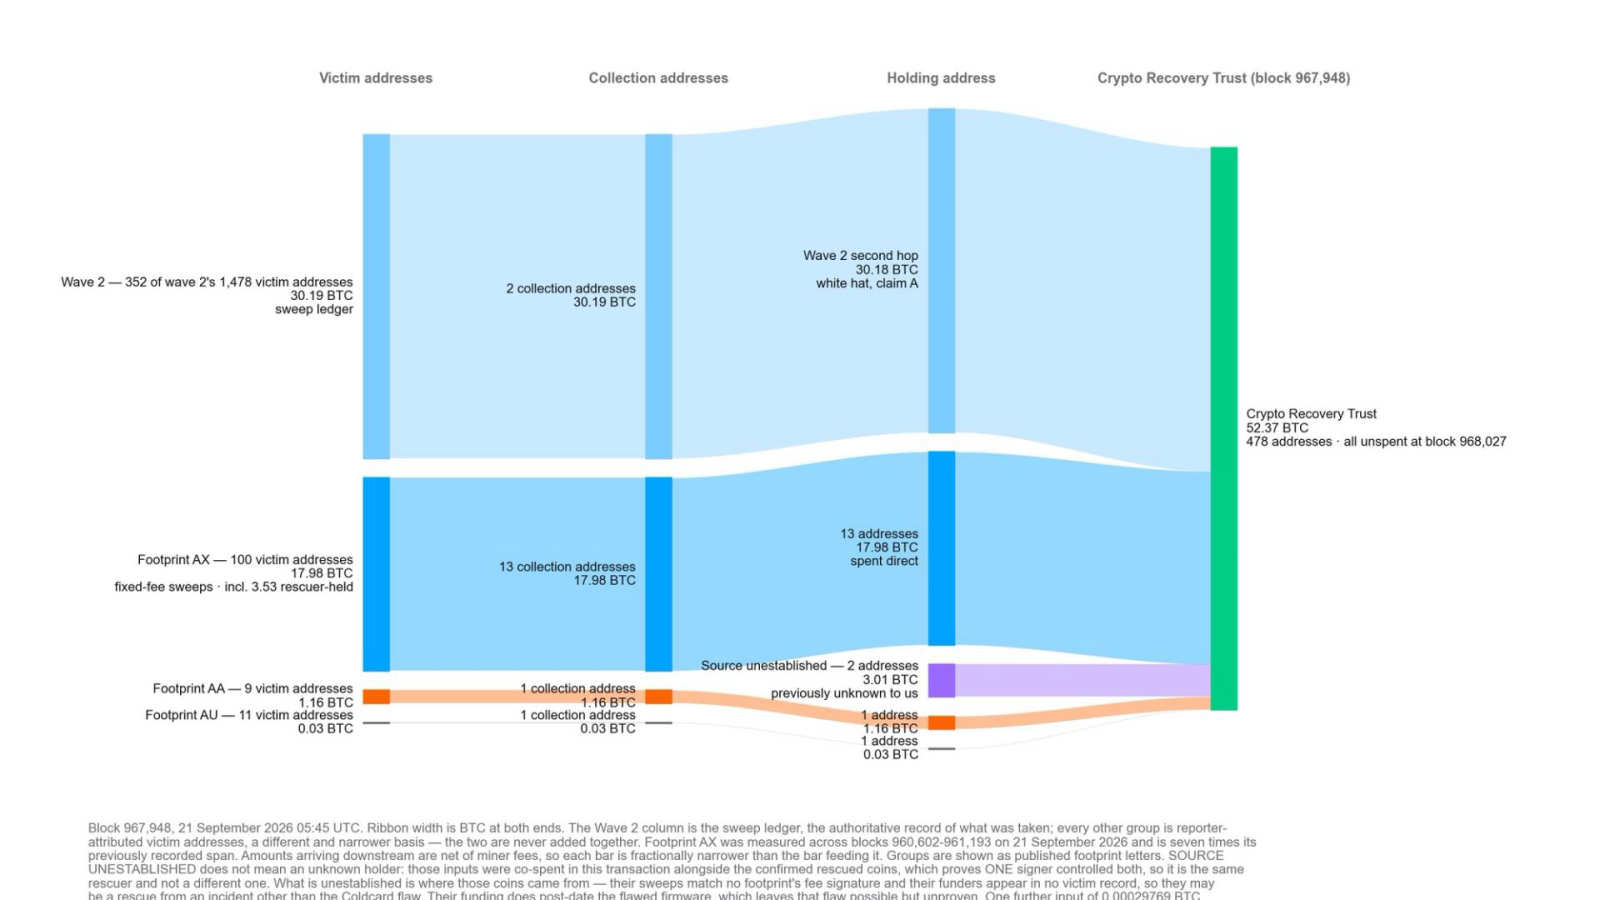
Not all of the bitcoin pulled from Coldcard wallets this summer ended up with a thief. Part of it was taken by people who want to return it, and this week 52.37 BTC of those funds was gathered at a single address.
According to Alex Thorn, Head of Research at Galaxy Digital, “whitehat operators” sent the coins to an address linked to a recovery trust set up only recently. It is the newest development in the aftermath of the Coldcard hardware wallet exploit that hit in July.
Whitehats got to the coins ahead of the attackers
Thorn explained that some of the bitcoin drained from victims’ wallets never reached malicious actors. It was taken by whitehats instead: ethical security professionals who put their hacking skills to work finding and fixing weaknesses.
Their aim in sweeping the funds was to hold them safely until they could go back to their owners. As rescues go, it is an unusual one. Moving someone else’s bitcoin without permission looks exactly like theft on-chain, and that is why this week’s tracking data carries weight.
The 52.37 BTC sweep originated in Wave 2 of the tracked exploit funds, and it also collected three footprints labeled AA, AU and AX. Everything was sent to an address with an OP_RETURN message reading “claim:cryptorecoverytrust dot com.” Block 967,948 confirmed the transaction.
Reading the figures
By Thorn’s count, the sum equals 2.8% of all tracked exploit funds. He added that roughly 40% of Wave 2 has so far been identified as whitehat activity.
The second number deserves the closer look, since it suggests a large portion of one attack wave may never have been theft in the first place.
In that same transaction, another 3.0134 BTC with no earlier tracking history also went into the CRT address. Thorn said this is presumably further Coldcard money recovered by whitehats, but he underlined that it has not been confirmed, so it should not yet be treated as recovered.
Inside the Coldcard exploit
The attack started on July 30, with further batches arriving over the following days. These were tracked as waves 1, 2 and 3, and estimated losses climbed past $100 million in bitcoin, with BTC trading at $84,251.41.
The weakness lay in how seeds were generated. Attackers used it to make wallets draw seeds from a weaker software-based random number source rather than the wallet’s dedicated random number generator, which let hackers reconstruct some of those seeds.
For a hardware wallet, that is a serious breakdown. A dedicated random number generator is among the core reasons people buy a device rather than storing keys in software.
Old seeds stay exposed after the patch
Coldcard maker Coinkite has since released patched firmware. Even so, funds held under seeds created before the fix remain at risk regardless of the update.
Updating the firmware repairs the generator, but it cannot repair a seed that was weak from the moment it was made. If your seed was created on the vulnerable firmware, an update on its own will not keep your coins safe.
Next steps for victims
Anyone affected can find out whether their funds were among those recovered by visiting cryptorecoverytrust.com and searching for their addresses.
An address that appears there means the funds are held by the trust rather than an attacker. If it does not appear and your seed was generated before the patch, transfer whatever remains to a freshly generated seed today.